The Biden administration is shifting to involve clients to be evaluated by a medical doctor in particular person just before receiving prescriptions for some controlled prescription drugs, which includes Adderall and OxyContin.
The proposal would reverse a policy enacted through the coronavirus pandemic that authorized physicians to prescribe these medicines via telehealth appointments. The move will make it much more challenging for Individuals to entry some prescription drugs employed for dealing with ache and psychological wellness disorders.
The Drug Enforcement Administration declared the proposed guidelines on Friday, which point out that telehealth flexibilities will be prolonged for frequent, non-controlled medicines but plan II medicines and narcotics will be prohibited with out an in-individual appointment.
Patients have to check out a health practitioner in human being at minimum once to acquire an first prescription for medicine the federal governing administration thinks have the maximum prospective for abuse, such as Vicodin, OxyContin, Adderall and Ritalin. Refills for these medicines could nevertheless be approved in excess of telehealth appointments.
NEW YORK NURSE ACCUSED OF SLAMMING Newborn On to BASSINET FIRED, Less than INVESTIGATION
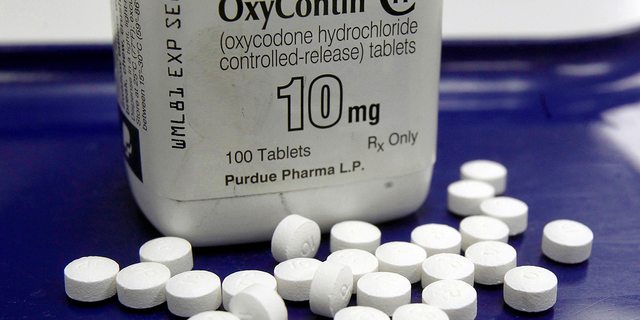
OxyContin supplements are organized for a picture at a pharmacy in Montpelier, Vermont.(AP Photo/Toby Talbot)
Health professionals will only be capable to prescribe managed remedies like Ambien and Xanaxas, as properly as medications applied to handle opioid habit, for 30 days. Any refills for these medications will need an in-particular person analysis.
The regulations intention to sustain expanded obtain to telehealth, which has been critical for hundreds of thousands of patients, notably all those dwelling in rural regions, when also balancing safety.
“DEA is dedicated to making sure that all Individuals can accessibility desired medicines,” DEA Administrator Anne Milgram claimed in a statement. “The permanent expansion of telemedicine flexibilities would continue larger access to treatment for clients across the nation even though making sure the protection of clients. DEA is dedicated to the growth of telemedicine with guardrails that stop the on the internet overprescribing of managed medicines that can cause harm.”
The shift arrives amid an ongoing opioid disaster and a developing selection of overdose deaths from managed drugs this kind of as fentanyl.
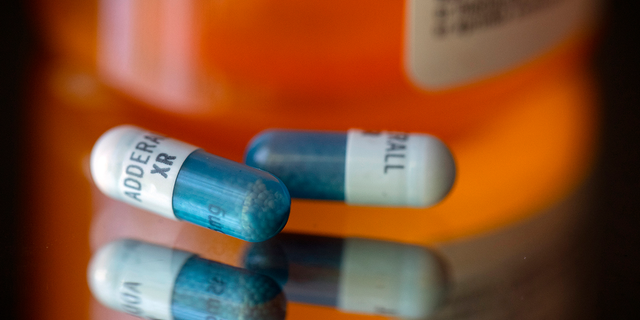
Adderall XR capsules are displayed in front of a drugs bottle.(AP Photo/Jenny Kane)
The DEA mentioned the proposed telemedicine procedures will advance its aim of increasing obtain to medication for opioid use ailment to anybody in the country who needs it.
“Medication for opioid use condition helps these who are battling to overcome material use condition by aiding persons obtain and maintain restoration and also avoid drug poisonings,” Milgram explained. “The telemedicine polices would continue on to develop access to buprenorphine for patients with opioid use problem.”
U.S. overdose deaths reached a document in 2021, and about a few-quarters of those had been from opioids. But the loss of life toll from synthetic opioids like fentanyl far exceeded people similar to prescription medicine that very same 12 months, according to Facilities for Condition Command data. Fentanyl is progressively existing in the black marketplace, as the capsules are normally pressed into phony prescription drugs or combined into other prescription drugs.
Facial area MASKS Produced ‘LITTLE TO NO DIFFERENCE’ IN Avoiding Spread OF COVID, SCIENTIFIC Review FINDS
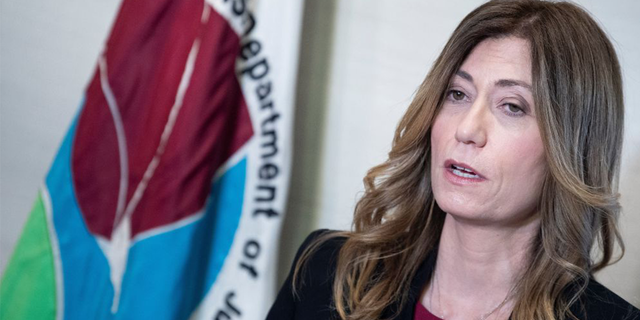
DEA Administrator Anne Milgram speaks at a push convention.(Getty)
Simply click In this article TO GET THE FOX News App
Quite a few states have presently moved to restore restrictions for telehealth treatment. As of October, just about 40 states and Washington, D.C., had ended emergency pandemic declarations making it easier for doctors to see patients in other states.
The proposed rules come just after startups in the telehealth sector launched in new many years to treat and prescribe drugs for mental wellness or focus deficit disorders. The marketplace and persons with difficulty accessing in-particular person treatment have mostly benefitted from the pandemic-period policy.
The new guidelines are anticipated to be in put before the COVID-19 public overall health emergency expires on May well 11.
When the covid-19 pandemic hit, Dr. Corey Siegel was additional organized than most of his peers.
50 percent of Siegel’s sufferers — several with non-public insurance and Medicaid — were previously employing telehealth, logging on to appointments via phones or pcs. “You get to meet up with their spouse and children associates you get to satisfy their pets,” Siegel reported. “You see far more into their lives than you do when they come to you.”
Siegel’s Medicare patients weren’t coated for telehealth visits till the pandemic drove Congress and regulators to temporarily shell out for distant health care remedy just as they would in-person care.
Siegel, segment main for gastroenterology and hepatology at Dartmouth-Hitchcock Health care Middle, is certified in a few states and many of his Medicare people had been regularly driving two to 3 several hours round journey for appointments, “which isn’t a modest feat,” he said.
The $1.7 trillion paying package deal Congress passed in December bundled a two-year extension of key telehealth provisions, this kind of as protection for Medicare beneficiaries to have telephone or movie health care appointments at house. But it also signaled political reluctance to make the payment modifications long-lasting, requiring federal regulators to examine how Medicare enrollees use telehealth.
The federal extension “basically just kicked the can down the road for two many years,” stated Julia Harris, associate director for the wellness program at the D.C.-based Bipartisan Policy Middle assume tank. At problem are inquiries about the price and cost of telehealth, who will gain from its use, and whether or not audio and video appointments should continue on to be reimbursed at the identical charge as confront-to-encounter treatment.
Right before the pandemic, Medicare paid out for only slim employs of remote drugs, these as emergency stroke treatment supplied at hospitals. Medicare also included telehealth for people in rural spots but not in their households — individuals ended up expected to journey to a selected site these as a medical center or doctor’s workplace.
But the pandemic brought a “seismic modify in perception” and telehealth “became a home time period,” reported Kyle Zebley, senior vice president of community coverage at the American Telemedicine Association.
The omnibus bill’s provisions include things like: paying out for audio-only and home care permitting for a assortment of medical doctors and many others, this kind of as occupational therapists, to use telehealth delaying in-particular person specifications for mental overall health sufferers and continuing current telehealth providers for federally experienced well being clinics and rural wellbeing clinics.
Telehealth use amid Medicare beneficiaries grew from less than 1{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} before the pandemic to a lot more than 32{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} in April 2020. By July 2021, the use of remote appointments retreated relatively, settling at 13{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} to 17{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} of promises submitted, in accordance to a charge-for-provider statements examination by McKinsey & Co.
Fears around possible fraud and the charge of expanding telehealth have made politicians hesitant, reported Josh LaRosa, vice president at the Wynne Wellbeing Team, which focuses on payment and care shipping reform. The report expected in the omnibus bundle “is genuinely going to enable to give extra clarity,” LaRosa said.
In a 2021 report, the Authorities Accountability Office environment warned that employing telehealth could maximize paying out in Medicare and Medicaid, and historically the Congressional Spending plan Business office has explained telehealth could make it less complicated for persons to use far more well being treatment, which would guide to additional paying.
Advocates like Zebley counter that distant treatment doesn’t automatically price tag extra. “If the priority is preventative care and expanding obtain, that must be taken into account when looking at prices,” Zebley reported, conveying that elevated use of preventative treatment could push down a lot more high priced expending.
Siegel and his colleagues at Dartmouth see distant treatment as a resource for serving to chronically ill patients get ongoing treatment and preventing pricey unexpected emergency episodes. It “allows clients to not be burdened by their health problems,” he stated. “It’s significant that we maintain this going.”
Some of Seigel’s operate is funded by The Leona M. and Harry B. Helmsley Charitable Have faith in. (The Helmsley Charitable Believe in also contributes to KHN.)
For the earlier 9 months, Dartmouth Health’s telehealth visits plateaued at additional than 500 for every working day. That’s 10{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} to 15{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} of all outpatient visits, reported Katelyn Darling, director of operations for Dartmouth’s virtual care centre.
“Patients like it and they want to continue accomplishing it,” Darling claimed, including that doctors — specially psychologists — like telehealth also. If Congress decides not to carry on funding for distant at-property visits immediately after 2024, Darling explained, she fears patients will have to drive yet again for appointments that could have been managed remotely.
The similar fears are worrying leaders at Sanford Health, which offers providers across the Higher Midwest.
“We definitely have to have those provisions to become long-lasting,” said Brad Schipper, president of virtual care at Sanford, which has health system associates, hospitals, clinics, and other amenities in the Dakotas, Iowa, and Minnesota. In addition to the provisions, Sanford is carefully looking at irrespective of whether medical professionals will go on to get paid out for supplying care throughout condition traces.
For the duration of the pandemic, licensing demands in states had been frequently relaxed to help health professionals to follow in other states and many of all those necessities are established to expire at the conclude of the community wellness emergency.
Licensing prerequisites were being not tackled in the omnibus, and to ensure telehealth accessibility, states need to have to allow for medical professionals to address people across condition lines, said Dr. Jeremy Cauwels, Sanford Health’s chief medical professional. This has been notably critical in delivering mental health care, he reported digital visits now account for about 20{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} of Sanford’s appointments.
Sanford is based mostly in Sioux Falls, South Dakota, and Cauwels recalled a person circumstance in which a affected individual lived four hrs from the closest youngster-adolescent psychiatrist and was “on the erroneous facet of the border.” Simply because of the latest licensing waivers, Cauwels stated, the patient’s wait for an appointment was minimize from several months to six times.
“We were in a position to get that child viewed with no Mom having a working day off to generate again and forth, with out a six-week hold off, and we had been able to do all the matters just about for that relatives,” Cauwels mentioned.
Psychiatrist Dr. Sara Gibson has utilised telehealth for many years in rural Apache County, Arizona. “There are some people today who have no accessibility to treatment without the need of telehealth,” she said. “That has to be additional into the equation.”
Gibson, who is also clinical director for Tiny Colorado Behavioral Health and fitness Centers in Arizona, said one critical query for policymakers as they search forward is not no matter if telehealth is superior than experience-to-encounter. It is “telehealth vs. no care,” she stated.
KHN (Kaiser Health News) is a national newsroom that creates in-depth journalism about health issues. Alongside one another with Policy Evaluation and Polling, KHN is a person of the 3 important functioning applications at KFF (Kaiser Spouse and children Basis). KFF is an endowed nonprofit organization supplying details on health difficulties to the country.
USE OUR Information
This tale can be republished for absolutely free (facts).
Open the website of Workit Health, and the path to treatment starts with a simple intake form: Are you in danger of harming yourself or others? If not, what’s your current opioid and alcohol use? How much methadone do you use?
Within minutes, patients looking for online treatment for opioid use and other addictions can complete the assessment and book a video visit with a provider licensed to prescribe suboxone and other drugs.
But what patients probably don’t know is that Workit was sending their delicate, even intimate, answers about drug use and self-harm to Facebook.
advertisement
A joint investigation by STAT and The Markup of 50 direct-to-consumer telehealth companies like Workit found that quick, online access to medications often comes with a hidden cost for patients: Virtual care websites were leaking sensitive medical information they collect to the world’s largest advertising platforms.
On 13 of the 50 websites, STAT and The Markup documented at least one tracker — from Meta, Google, TikTok, Bing, Snap, Twitter, LinkedIn, or Pinterest — that collected patients’ answers to medical intake questions. Trackers on 25 sites, including those run by industry leaders Hims & Hers, Ro, and Thirty Madison, told at least one big tech platform that the user had added an item like a prescription medication to their cart, or checked out with a subscription for a treatment plan.
advertisement
The trackers that STAT and The Markup were able to detect, and what information they sent, is a floor, not a ceiling. Companies choose where to install trackers on their websites and how to configure them. Different pages of a company’s website can have different trackers, and this analysis did not test every page on each company’s site.
All but one website examined sent URLs users visited on the site and their IP addresses — akin to a mailing address for a computer, which can be used to link information to a specific patient or household — to at least one tech company. The only telehealth platform that the analysis did not find sharing data with outside tech giants was Amazon Clinic, a platform recently launched by Amazon.
Health privacy experts and former regulators said sharing such sensitive medical information with the world’s largest advertising platforms threatens patient privacy and trust and could run afoul of unfair business practices laws. They also emphasized that privacy regulations like the Health Insurance Portability and Accountability Act (HIPAA) were not built for telehealth. That leaves “ethical and moral gray areas” that allow for the legal sharing of health-related data, said Andrew Mahler, a former investigator at the U.S. Department of Health and Human Services’ Office for Civil Rights.
“I thought I was at this point hard to shock,” said Ari Friedman, an emergency medicine physician at the University of Pennsylvania who researches digital health privacy. “And I find this particularly shocking.”
In October and November, STAT and The Markup signed up for accounts and completed onboarding forms on 50 telehealth sites using a fictional identity with dummy email and social media accounts. To determine what data was being shared by the telehealth sites as users completed their forms, reporters examined the network traffic between trackers using Chrome DevTools, a tool built into Google’s Chrome browser.
On Workit’s site, for example, STAT and The Markup found that a piece of code Meta calls a pixel sent responses about self-harm, drug and alcohol use, and personal information — including first name, email address, and phone number — to Facebook.
The investigation found trackers collecting information on websites that sell everything from addiction treatments and antidepressants to pills for weight loss and migraines. Despite efforts to trace the data using the tech companies’ own transparency tools, STAT and The Markup couldn’t independently confirm how or whether Meta and the other tech companies used the data they collected.
After STAT and The Markup shared detailed findings with all 50 companies, Workit said it had changed its use of trackers. When reporters tested the website again on Dec. 7, they found no evidence of tech platform trackers during the company’s intake or checkout process.
“Workit Health takes the privacy of our members seriously,” Kali Lux, a spokesperson for the company, wrote in an email. “Out of an abundance of caution, we elected to adjust the usage of a number of pixels for now as we continue to evaluate the issue.”
“Advertisers should not send sensitive information about people through our Business Tools,” Dale Hogan, a spokesperson for Meta, wrote in an email.
Patients may assume that health-related data is always protected by privacy regulations including HIPAA. Workit, for one, begins its intake form with a promise that “all of the information you share is kept private and is protected by our HIPAA-compliant software.”
“The very reason why people pursue some of these services online is that they’re seeking privacy,” said David Grande, a digital health privacy researcher at the University of Pennsylvania.
But the reality online is more complex, making it all but impossible for the average user to know whether the company they’re entrusting with their data is obligated to protect it. “Individually, we have a sense that this information should be protected,” said Mahler, who is now vice president of privacy and compliance at CynergisTek, a health care risk auditing company. “But then from a legal and a regulatory perspective, you have organizations saying … technically, we don’t have to.”
Rather than providing care themselves, telehealth companies often act as middlemen connecting patients to affiliated providers covered by HIPAA. As a result, information collected during a telehealth company’s intake may not be protected by HIPAA, while the same information given to the provider would be.
“All the privacy risks are there, with the mistaken but entirely reasonable illusion of security,” said Matthew McCoy, a medical ethics and health policy researcher at the University of Pennsylvania. “That’s a really dangerous combination of things to force the average consumer to deal with.”
In response to questions for this story, representatives of Meta, Google, TikTok, Bing, Snap, and Pinterest said advertisers are responsible for ensuring they aren’t sending sensitive information via the tools. Twitter did not respond to requests for comment.
“Doing so is against our policies and we educate advertisers on properly setting up Business tools to prevent this from occurring,” wrote Meta’s Hogan. “Our system is designed to filter out potentially sensitive data it is able to detect.”
LinkedIn’s tracker “collects URL information which we immediately encrypt when it reaches our servers, delete within 7 days and do not add to a profile,” Leonna Spilman, a spokesperson for the company, wrote in an email.
Nevertheless, three of the seven big tech companies also said they had taken action to investigate or stop the data sharing.
Google is “currently investigating the accounts” in question, spokesperson Elijah Lawal wrote in an email.
“In response to this new information, we have paused data collection from these advertisers’ sites while we investigate,” Snap spokesperson Peter Boogaard wrote in an email.
Pinterest “offboarded the companies in question,” spokesperson Crystal Espinosa wrote in an email.
A boom industry on the edge of the law
Together, the companies in this analysis reflect an increasingly competitive — and lucrative — direct-to-consumer health care market. The promise of a streamlined, private prescription process has helped telehealth startups raise billions as they seek to capitalize on a pandemic-driven boom in virtual care.
Hims & Hers, one of the largest players in the space, is now a publicly traded company valued at more than $1 billion; competitor Ro has raised $1 billion since its founding in 2017, with investors valuing the company at $7 billion. Thirty Madison, which operates several telehealth companies focused on different medical needs, is valued at more than $1 billion.
The industry’s rapid growth has been enhanced by its ability to use data from tools like pixels to target advertisements to increasingly specific patient populations and to put ads in front of users who have visited their site before. The companies we analyzed mostly provide care and prescriptions for conditions like migraines, sexual health, or mental health disorders rather than comprehensive primary or urgent care — making browsing their websites inherently sensitive.
In the same way visiting an opioid use disorder treatment center can identify an individual as an addiction patient, data about someone visiting a telehealth site that treats only one condition or provides only one medication can give advertisers a clear window into that person’s health. Direct answers to onboarding forms could be even more valuable because they’re more detailed and specific, said McCoy. “And it’s more insidious because I think it would be all that much more surprising to the average person that information that you put in a form wouldn’t be protected. It’s both worse and more unexpected.”
Consider the form for Thirty Madison’s Cove, which offers migraine medications. It prompts visitors to share details about their migraines, past diagnoses, and family history — and during our testing sent the answers to Facebook and Google. If a user added a medication to the cart, detailed information about the purchase, including the drug’s name, dose, and price, were also sent to Facebook, along with the user’s hashed full name, email, and phone number.
While hashing obscures those details into a string of letters and numbers, it does not prevent tech platforms from linking them to a specific person’s profile, which Facebook explicitly says it does before discarding the hashed data.
A Google tracker collects answers to medical screening questions on Cove’s website.
A tracker tells Facebook when a user adds a medication to the cart. It also sends the user’s hashed name, email, and phone number.
“It’s a pure monetization play,” said Eric Perakslis, chief science and digital officer at the Duke Clinical Research Institute. “And yes, everybody else is doing it, it’s the way the internet works. … But I think that it’s out of step with medical ethics, clearly.”
In particular, experts worry that health data could be used to target patients in need with ads for services and therapies that are unnecessary or even harmful.
The big tech platforms that responded for this story say they do not allow targeted advertising based on specific health conditions, and some telehealth companies said they only use the data collected to measure the success of their advertising. However, as The Markup has previously reported, advertisers may still be able to target ads on Facebook using terms that are close proxies for health conditions.
On 35 of the 50 websites, STAT and The Markup found trackers sending individually identifying information to at least one tech company, including names, email addresses, and phone numbers.
That presents patients with a Catch-22. “It requires anyone that wants to take advantage of telehealth … to expose a lot of the same information that they would reveal within a protected health care relationship,” said Woodrow Hartzog, a privacy and technology law professor at Boston University — but without the same protections.
In recent months, regulators have begun cracking down on the indiscriminate collection and sale of personal health data.
After issuing a warning to businesses about selling health information in July, the Federal Trade Commission sued data broker Kochava, alleging that the company put consumers at risk by failing to protect location data that could reveal sensitive details about people’s health, such as a visit to a reproductive health clinic or addiction recovery center. Kochava has asked for the case to be dismissed and countersued the FTC.
The increased attention reflects growing fears about how health data may be used once it enters the black boxes of corporate data warehouses — whether it originates from a hospital, a location tracker, or a telehealth website.
“The health data market just continues to kind of spiral out of control, as you’re seeing here,” said Perakslis.
But thanks to their business structures, many of the companies behind telehealth websites appear to be operating on the outskirts of health privacy regulations.
‘It does seem deceptive’
When users visit Cerebral, a mental health company whose prescribing and business practices came under federal investigation this year, they are required to answer a series of “clinically tested questions” that can cover a wide range of conditions, including depression, anxiety, bipolar disorder, and insomnia. During testing, with every response — such as clicking a button to indicate feeling depressed “more than half the days” over the last two weeks — a pixel sent Facebook the text of the answer button, the specific URL the user was visiting when clicking the button, and the user’s hashed name, email address, phone number.
At a doctor’s office, that kind of detail collected on an intake form would likely be subject to HIPAA. But as with most of the telehealth companies in this analysis, Cerebral Inc. itself doesn’t provide care; its website connects patients with providers like those employed by Cerebral Medical Group, P.A. and others. While those medical groups are HIPAA-covered entities that cannot share protected health information with third parties except under narrow circumstances, Cerebral claims in its privacy policy to be a go-between that is not covered by HIPAA — except in limited cases when it acts as a business associate of a medical group, pharmacy, or lab.
Cerebral did not answer detailed questions that would clarify what these cases might be. But in a Nov. 30 email, spokesperson Chris Savarese said the company would adjust its use of tracking tools. “We are removing any personally identifiable information, including name, date of birth, and zip code from being collected by the Meta Pixel,” he wrote.
However, when STAT and The Markup tested Cerebral’s website again on Dec. 7, reporters found that a Meta Pixel was still sending answers to some intake questions and hashed names to Facebook, and trackers from Snap and Pinterest were also collecting hashed email addresses.
A Facebook tracker collected answers from a Cerebral intake form during an October test by STAT and The Markup.
During a December test, a Facebook tracker was still collecting Cerebral’s intake form answers.
The telehealth companies that responded to detailed queries said their data-sharing practices adhered to their privacy policies. Those kinds of policies commonly include notice that some — but not all — health data shared with the site is subject to HIPAA. Many companies responded that they were careful to ensure that data shared via third-party tools was not considered protected health information.
But the structure of the companies’ businesses — and the inscrutable language in their privacy policies and terms of use — make it difficult for consumers to know what data would qualify as protected, and when.
“There is so much intransparency, and that makes it complex and maybe even deceptive for consumers,” said Sara Gerke, a professor of health law and policy at Penn State Dickinson Law.
Several telehealth companies claimed that the information collected from their websites was not personally identifiable because it was hashed. HIPAA allows health information to be shared when it has been de-identified. However, hashing does not anonymize data for the tech platforms that receive it and match it to user profiles. And every data packet sent by a tech company’s tracker includes the user’s IP address, which is one of several unique identifiers that explicitly qualify health data for protection under HIPAA.
Further complicating decisions for patients, at least 12 of the direct-to-consumer companies examined in this investigation promise on their websites that they are “HIPAA-compliant.” That could encourage users to think all the data they share is protected and lead them to divulge more, said Hartzog. Yet the regulations apply to the websites’ data use only in limited cases.
Monument, a site that offers alcohol treatment, starts its intake form by saying, “Any information you enter with Monument is 100{bf0515afdcaddba073662ceb89fbb62b6b1bf123143c0e06b788e1946e8c353f} confidential, secure, and HIPAA compliant.” Yet in its responses to STAT and The Markup, it said that it does not consider information transmitted to third parties from that form — including answers to questions like “In the past year, have you continued to drink even though it was making you feel depressed or anxious or adding to another health problem? or after having had a memory blackout?” — to be protected health information under HIPAA.
“If they’re not covered by HIPAA and they have a HIPAA-compliant badge, that seems like a case the FTC could bring,” said Justin Brookman, the director of technology policy for Consumer Reports and former policy director with the FTC, which has previously charged companies for deceptive use of HIPAA-compliant badges. “There’s an implication there that you’re regulated in certain ways, that your data is protected, and so it does seem deceptive.”
Such data sharing could be particularly damaging to patients seeking care for substance use disorders, said Jacqueline Seitz, senior staff attorney for health privacy at the Legal Action Center — especially if it enters opaque data brokerages where it can be resold and repurposed indefinitely.
Several companies in this analysis are capitalizing on federal waivers activated during the pandemic that allow controlled substances like suboxone, which is used to treat opioid use disorder, to be prescribed virtually. Under federal law, qualifying addiction treatment providers — including those that prescribe suboxone — are held to patient privacy standards even stricter than HIPAA. For example, Workit’s physician group states it is forbidden from acknowledging “to anyone outside of the program that you are a patient or disclos[ing] any information identifying you as a substance use disorder patient” except in narrow situations.
Nonetheless, STAT and The Markup found that Workit and other telehealth companies — in their role connecting patients to providers — share information that identifies a user as someone seeking addiction treatment. On Boulder Care’s website, a pixel sent Facebook our name and email when we joined a suboxone treatment program waitlist. And trackers on the website of Bicycle Health, another online suboxone provider, notified Google and Bing that our email address had been entered on an “enrollment confirmation” URL.
Boulder Care chief operating officer Rose Bromka said the company had started improving its “website hygiene” before being contacted for this article, and restricted the information sent by the Meta pixel after reviewing our findings.
However, Bromka added that Boulder still tracks some information about website visitors to guide its advertising.
“We are always looking to balance ensuring we are able to get the word out about options with holding to our value set,” she said.
Big tech’s black boxes
Meta, Google, TikTok, Bing, LinkedIn, Snap, and Pinterest say they have policies against using sensitive health data to help target advertisements.
“We clearly instruct advertisers not to share certain data with us and we continuously work with our partners to avoid inadvertent transmission of such data,” TikTok spokesperson Kate Amery wrote in an email, adding, “[W]e also have a policy against targeting users based on their individual health status.”
Meta and Google claim to have algorithmic filters that identify and block sensitive health information from entering their advertising systems. But the companies did not explain how those systems work or their effectiveness. By Facebook’s own admission to investigators from the New York Department of Financial Services in 2021, its system was “not yet operating with complete accuracy.”
To trace what happened to data collected by trackers, STAT and The Markup created dummy accounts logged into Facebook, TikTok, and Twitter while testing the telehealth websites. Reporters then used the platforms’ “download your data” tools in an attempt to determine whether any health information the trackers collected was added to our profiles.
The information provided by those tools was so limited, however, that STAT and The Markup couldn’t confirm how or whether the sensitive health information was used.
For example, a Meta Pixel on RexMD, which prescribes erectile dysfunction drugs, collected the name of the medication in our cart, our email, gender, and date of birth. Facebook’s transparency tool, however, only showed 10 “interactions” on RexMD’s website, with generic descriptions like “ADD_TO_CART.” It did not provide details about the specific data Facebook ingested during those interactions. A TikTok pixel collected some of that same information from RexMD, but TikTok’s report on our “usage data from third-party apps and websites” had just one line: “You have no data in this section.”
Our Twitter data showed that the company knew the dummy account user had selected a product on RexMD’s website and the exact URL on which that product was selected.
On some websites, users’ data was also being collected by “custom events,” meaning that a website owner deliberately created a custom tracking label that could have a phrase such as “checkout” in it but wouldn’t necessarily show up in the tech platforms’ transparency tools.
Only four companies answered whether they had ever been notified by Facebook of potentially sensitive health information. Monument and Favor had data flagged but said they determined it wasn’t sensitive. Lemonaid received a notification in error related to a promotional code, and Boulder Care had received none.
Telehealth websites should be held accountable for the trackers they install, said Hartzog, the Boston University law professor. But “big platforms that are deploying these surveillance technologies also need to be held accountable, because they’re able to vacuum up every ounce of personal data on the internet in the absence of a rule that tells them not to.”
The companies in this investigation said their services fill an important need. “The makeup of the traditional health care system has in many cases prevented people from accessing treatment for conditions that should be easy to treat,” Scott Coriell, a spokesperson for Hims & Hers, wrote in an email. Companies that serve patients with mental health or substance use disorders emphasized that long wait times to see in-person providers, and the stigma associated with seeking care, made virtual services especially valuable.
Marketing supported by third-party tracking is part of making that care accessible, some argued. “Monument uses online advertising platforms to raise awareness of our evidence-based treatment for alcohol use disorder, and get people the support and relief they deserve,” wrote CEO Michael Russell. “We transmit the minimum amount of data required to allow us to track the effectiveness of our advertising campaigns.” Favor spokesperson Sarah Abboud argued that calling standard industry practices into question could threaten trust in those services.
But health privacy and policy experts see a disconnect between the industry’s stated emphasis on privacy and its data-sharing practices. “Telemedicine providers should have realized from the get-go that if their entire business model is to seamlessly move people from marketing to care and the care will be online, then there’s going to be more personal identifiable information submitted and thus more privacy risk and thus more privacy liability,” said Christopher Robertson, a health law and policy professor at Boston University.
One problem may be that marketing teams don’t fully understand privacy regulations, and legal teams don’t have a handle on how the marketing tools work.
Sara Juster, privacy officer for the weight-loss telehealth company Calibrate, wrote in an email that the company doesn’t “send any health information collected in our eligibility flow back to platforms.” But a Meta Pixel on its site sent data including height, weight, BMI, and other diagnoses, like diabetes, to Facebook. Juster then clarified the pixel was a duplicate that should have been removed in a tracking audit earlier this year.
However, as of Dec. 7, a Meta Pixel was still present on the site and sharing hashed identifiers and checkout events with Facebook. The pixel appeared to have been reconfigured, though, to send less information than it had during our original testing.
Without updated laws and regulations, experts said patients are left to the whims of rapidly evolving telehealth companies and tech platforms, who may choose to change their privacy policies or alter their trackers at any time.
“It doesn’t make any sense that right now, we only have protections for sensitive health information generated in certain settings,” said McCoy, “but not what can be equally sensitive health information generated in your navigation of a website, or your filling out of a very detailed form about your history and your prescription use.”
This article was co-reported with The Markup, a nonprofit newsroom that investigates how powerful institutions are using technology to change our society. Sign up for its newsletters here.